Apple patches high-severity eavesdropping vulnerability in Beats Studio Buds
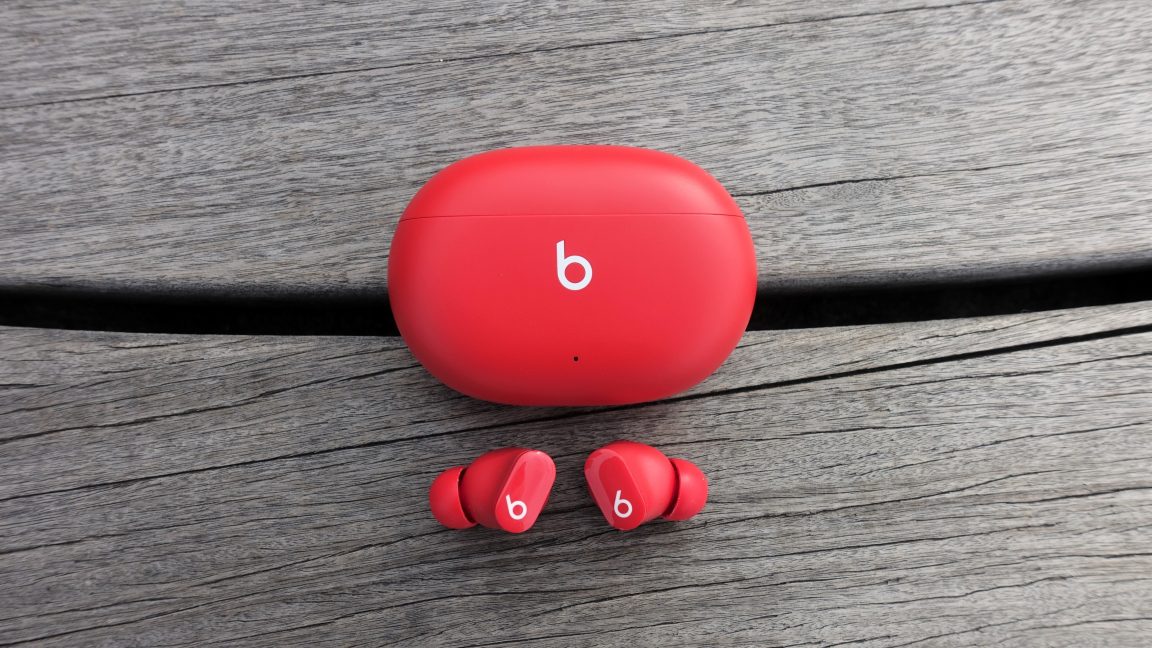
Apple has updated its Beats Studio Buds wireless earbuds to patch a high-severity vulnerability that could be exploited by nearby hackers to eavesdrop on users.
The vulnerability, CVE-2025-20701, allowed improper authentication in the firmware running on the Bluetooth-related chips, enabling people within signal range to impersonate devices that had previously been paired with the earbuds. The researchers demonstrated this in a series of end-to-end attacks that allowed them to eavesdrop on conversations or sounds within earshot of the phone microphone.
Apple joins the patch party
“Impact: An attacker within Bluetooth range may be able to listen through the microphone of a device which is not yet paired and actively seeking pair requests,” Apple said in a Tuesday security advisory. The fix is contained in Beats Firmware Update 1B211, which is delivered automatically while headphones are paired with and within Bluetooth range of a user’s iPhone, iPad, or Mac. Users can check their firmware version by going to Settings on their device, navigating to Bluetooth, and tapping the info button next to the headphones.
Carrying a severity rating of 8.8 out of 10, CVE-2025-20701 was one of three vulnerabilities resulting from last year’s disclosure by researchers Dennis Heinze and Frieder Steinmetz of security firm Insinuator about chips made by Airoha Systems. In response, Airoha released an updated software development kit to affected hardware sellers. Apple’s incorporation of the patch into the Beats Studio Buds came the same week that Jabra, another affected headphone manufacturer, also announced patched versions. According to this article from Ecoustics, manufacturers Bose and JBL have released statements saying their devices have also been updated to incorporate the fixes.
Security firm Sentinel One has a deeper dive into CVE-2025-20701 here.
Heinze and Steinmetz said last year that the full chain of attacks gave attackers the ability to do other malicious things, including retrieving call history and contacts, and even calling arbitrary numbers. Many of those capabilities are dependent on the specific devices being paired, since the functionality built into them differs from platform to platform.
Devices affected by the Airoha vulnerabilities are by no means alone. In January, researchers disclosed WhisperPair, a series of vulnerabilities that allows an attacker to hijack Bluetooth devices connected through Google Fast Pair, a proprietary protocol belonging to the company. Besides eavesdropping, attackers can exploit the WhisperPair flaws to geolocate devices. The vulnerabilities affect more than a dozen devices from 10 manufacturers, including Sony, Nothing, JBL, OnePlus, and Google itself.
There are few, if any, reports of Bluetooth vulnerabilities like these being actively exploited in the wild. The complexity of such attacks is often high, and an attacker has to continually stay within Bluetooth range of a target while utilizing the exploit. People who think they may be targeted by such attacks should turn off Bluetooth in devices whenever they’re not needed, and remain aware of the risks when Bluetooth is enabled.
 1.
Supersonic airliner in doubt as company shifts to powering AI data centers
Related Topics
Keywords
Related Stories
North Korea linked to massive Binance crypto heist
The FBI says North Korea was behind the massive $6.3 billion crypto heist that hit Binance on October 29th. The FBI labeled the activity "TraderTraitor" and said that it had observed actors it has connected to hack converting the tokens to Ethereum and preparing for further…

HomePod Mini 2 first look: Three things I love and one disappointment
Apple’s second-generation HomePod Mini is a nice upgrade, but the biggest improvement hasn’t arrived yet. | Photo: Jennifer Pattison Tuohy / The Verge When I first heard about the new $149 HomePod Mini 2 at Apple's Welcome Home event last month, I was disappointed. It's been six…

Prop 45 in California could be hiding a loophole for data centers
A high-stakes California ballot measure pitched as a fast track for "essential" infrastructure could wind up giving data center developers a loophole to evade public scrutiny, environmental advocates warn. Proposition 45 would shorten timelines for state-mandated environmental…

New Zelda and GTA represent a games industry that no longer exists
This is The Stepback, a weekly newsletter breaking down one essential story from the tech world. For more on the biggest game releases of the year, follow Andrew Webster. The Stepback arrives in our subscribers' inboxes on Sunday at 8AM ET. Opt in for The Stepback here. How it…

Top Stories

CSOs urge judiciary to avoid another Imo-style embarrassment in Uzodimma’s Senate case

Spence 'very proud' to break WSL appearance record

Referee accidentally fractures college football player's leg

Freedom advocates urge Nigeria to grant Africans visa-free entry
Iran warns next war with US could be longer as Trump threatens further strikes
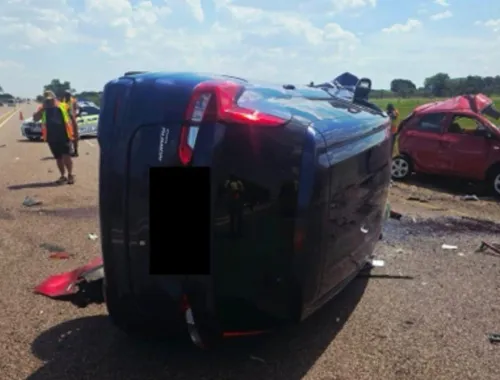
Two women killed in N1 crash near Kranskop as highway closed
AFFORDABLE HOUSING OP-ED: CT’s Tafelberg social housing units cut by Heritage assessment

Five teenagers stabbed at Halloween party
Latest
CSOs urge judiciary to avoid another Imo-style embarrassment in Uzodimma’s Senate case
Spence 'very proud' to break WSL appearance record
Referee accidentally fractures college football player's leg
Freedom advocates urge Nigeria to grant Africans visa-free entry
Iran warns next war with US could be longer as Trump threatens further strikes
Two women killed in N1 crash near Kranskop as highway closed
AFFORDABLE HOUSING OP-ED: CT’s Tafelberg social housing units cut by Heritage assessment
Five teenagers stabbed at Halloween party